WebAuthn Passkeys: Secure Passwordless Login for Web Apps
By: Md Tarek · 17 Oct 2026
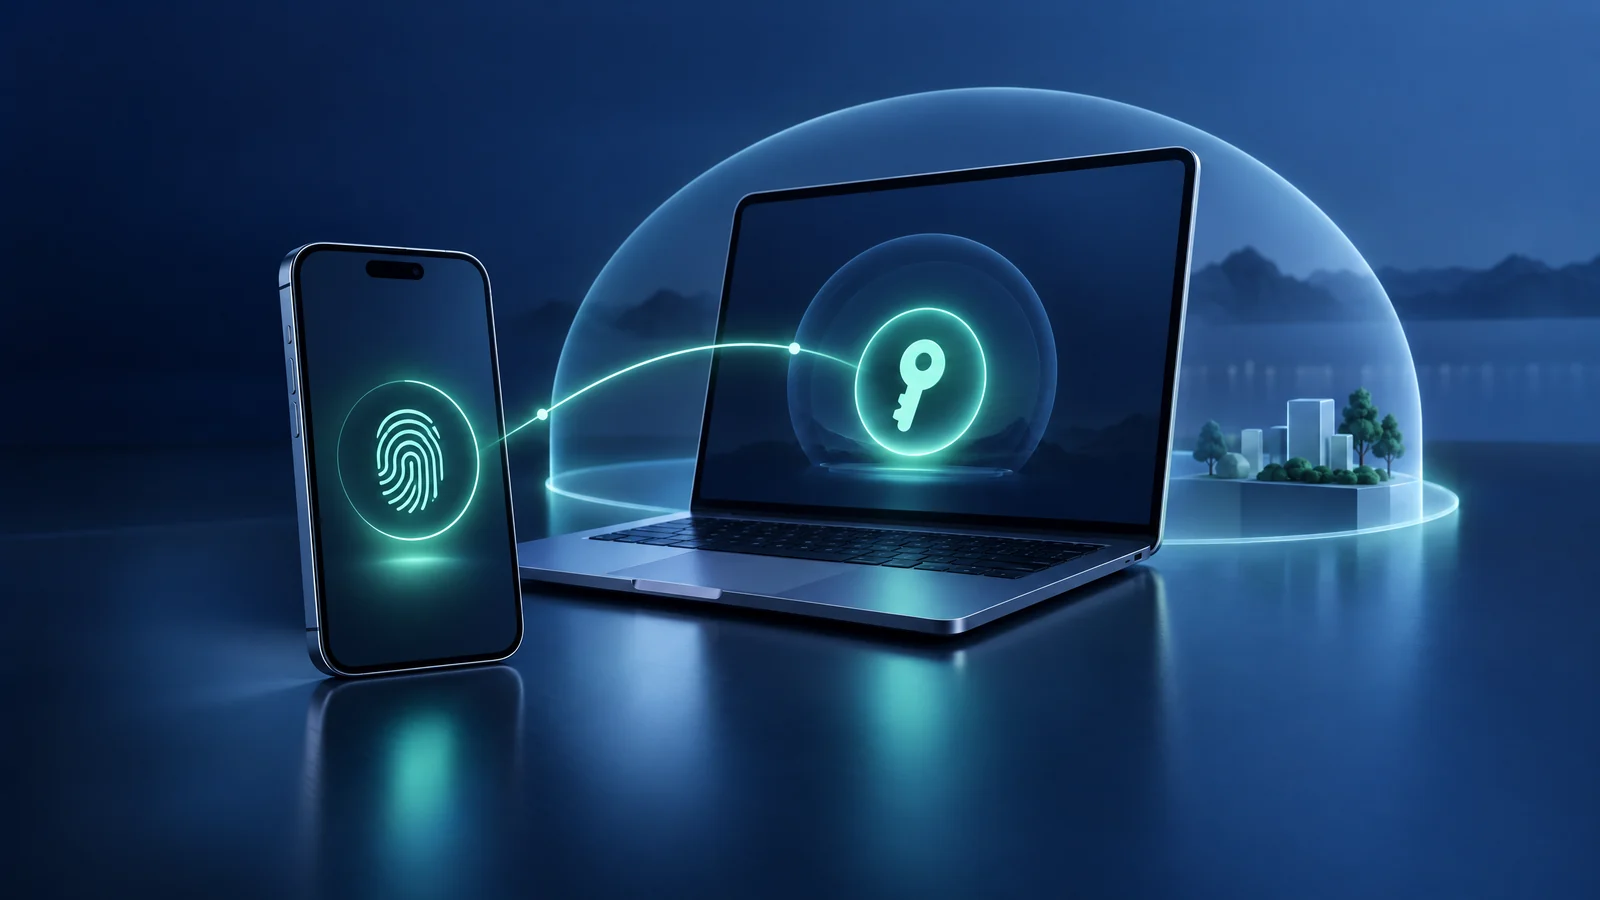
Yes. WebAuthn passkeys let a web app replace password entry with a public-key challenge that the user approves with a device unlock, such as a fingerprint, face scan, PIN, or security key. The server keeps a public key, while an authenticator or passkey provider keeps the corresponding private key. Because the browser binds the signature to the site’s origin, a fake login page cannot normally reuse the response at the real site. [1] [2]
What a passkey changes
A passkey is a discoverable WebAuthn credential designed for sign-in without a typed password. WebAuthn is the browser API; the relying party (RP) is your web application and its server; and the authenticator is the device, security key, or password manager that creates and uses the key pair. A passkey provider may also sync eligible credentials across a user’s devices. [2] [3] [5]
This model changes what a database breach exposes. The RP needs the credential ID, the user association, and the public key needed to verify signatures. The private key is managed by the authenticator or provider and is not a password hash that the application can retrieve. However, do not promise that every passkey is hardware-backed or device-bound: synchronized credentials and provider implementations have different properties. [2] [3]
Registration: create and store the credential
Registration should begin only after the account has been identified and the user has been authenticated strongly enough to authorize a new login method. The server then creates a fresh, unpredictable challenge and sends WebAuthn creation options to the browser. Those options normally include a stable, opaque user ID, a display name, the RP name and ID, accepted public-key algorithms, and excludeCredentials so a user does not accidentally register the same credential twice. [1] [4]
A minimal browser call, after the server’s JSON has been decoded into the API’s binary types, looks like this:
const credential = await navigator.credentials.create({
  publicKey: {
    challenge,                 // fresh bytes from the server
    rp: { id: "example.com", name: "Example" },
    user: { id: userHandleBytes, name: username, displayName },
    pubKeyCredParams: [{ type: "public-key", alg: -7 }],
    excludeCredentials,
    authenticatorSelection: {
      residentKey: "required",
      userVerification: "preferred"
    }
  }
});
The frontend sends the resulting credential to the server. Server-side WebAuthn code must verify the response before saving anything: confirm that the ceremony type is registration, the challenge matches the short-lived server record and current session, the expected origin is present, the RP ID hash is correct, and the attestation data and public-key signature are valid. After that, store the credential ID, public key, user ID, creation metadata, and (where applicable) the authenticator counter. Use a maintained server library rather than implementing CBOR parsing and signature verification yourself. [1] [2] [4]
Authentication: sign a one-time challenge
For login, the server creates another random challenge. A discoverable passkey can let the browser present account choices without first receiving a credential ID; a non-discoverable flow can send an allowCredentials list. The browser calls navigator.credentials.get({ publicKey: { challenge, rpId, ... } }), and the authenticator asks for local user verification according to the requested policy. [2] [4]
The response is an assertion, not a reusable token. The server looks up the credential by ID, validates the client-data type, exact challenge, expected origin, RP ID hash, user-verification flag when required, and signature over the authenticator data and client-data hash. It then verifies that signature with the stored public key, checks the counter according to the library’s guidance, and only then creates or rotates the application session. A challenge must be single-use, bound to the intended login, and expired if the ceremony is abandoned; otherwise an intercepted response could be replayed. [1] [2] [5]
Origin, RP ID, and deployment boundaries
Origin and RP ID are related but not interchangeable. An origin includes scheme, host, and port, such as https://login.example.com:443. An RP ID is a domain string and does not include scheme or port. By default it is derived from the caller’s effective domain, but an explicitly chosen RP ID must be the origin’s domain or a registrable suffix, such as example.com for login.example.com. [1]
That choice is a security and migration decision. A credential scoped to example.com can be used by eligible subdomains, while login.example.com narrows the scope. Configure one canonical HTTPS origin, keep the RP ID consistent across registration and login, and test every hostname, reverse proxy, and staging environment separately. WebAuthn is exposed only in secure contexts, with localhost treated specially for development. [1] [2]
Recovery and fallback are part of the design
A passkey can be lost with a device, account, or provider. Offer users a way to register more than one passkey, including a recovery device or hardware security key, and provide a credential-management screen that can revoke an individual credential. Notify users when a passkey is added or removed. Recovery must be at least as strong as the account it protects: a weak email-only reset can become the easiest bypass around phishing-resistant login. OWASP recommends re-authentication after account recovery, device enrollment, suspicious activity, and other high-risk changes. [3] [4]
During migration, keep a carefully secured fallback such as an existing password plus an additional factor, or a verified account-recovery process. This improves compatibility for older browsers and users who have not enrolled a passkey, but it also preserves the attack surface of that fallback. Apply rate limits, phishing-resistant options where possible, session rotation, and step-up authentication for changing passkeys or recovery data. [3] [5]
Common mistakes to avoid
- Trusting the client: the browser transports the response; only the server verifies it.
- Accepting any origin or RP ID: compare against an explicit allowlist for the deployment.
- Reusing challenges: generate them server-side, bind them to a session and ceremony, expire them, and reject reuse.
- Storing only a username: persist each credential ID and public key because one account can have several passkeys.
- Assuming biometrics are the secret: biometric or PIN verification unlocks an authenticator; the server still verifies a signature.
- Deleting the fallback too early: phase out weaker methods only after recovery, device coverage, and support procedures work.
FAQs
Are passkeys really passwordless?
Yes, when the RP uses a passkey as the primary credential. The user still unlocks a device or authenticator, but the web app receives a signed assertion rather than a typed password. [2]
Should a server store a passkey’s private key?
No. Store the credential ID and public key needed for verification, never a private key supplied by the browser. Let the authenticator or passkey provider manage private-key operations. [1] [2]
References
[1] Web Authentication: An API for accessing Public Key Credentials - Level 3
[2] Web Authentication API - MDN Web Docs
[3] Authentication Cheat Sheet - OWASP