Secure File Uploads: Validate, Quarantine, Store, and Authorize
By: Md Tarek · 17 Oct 2026
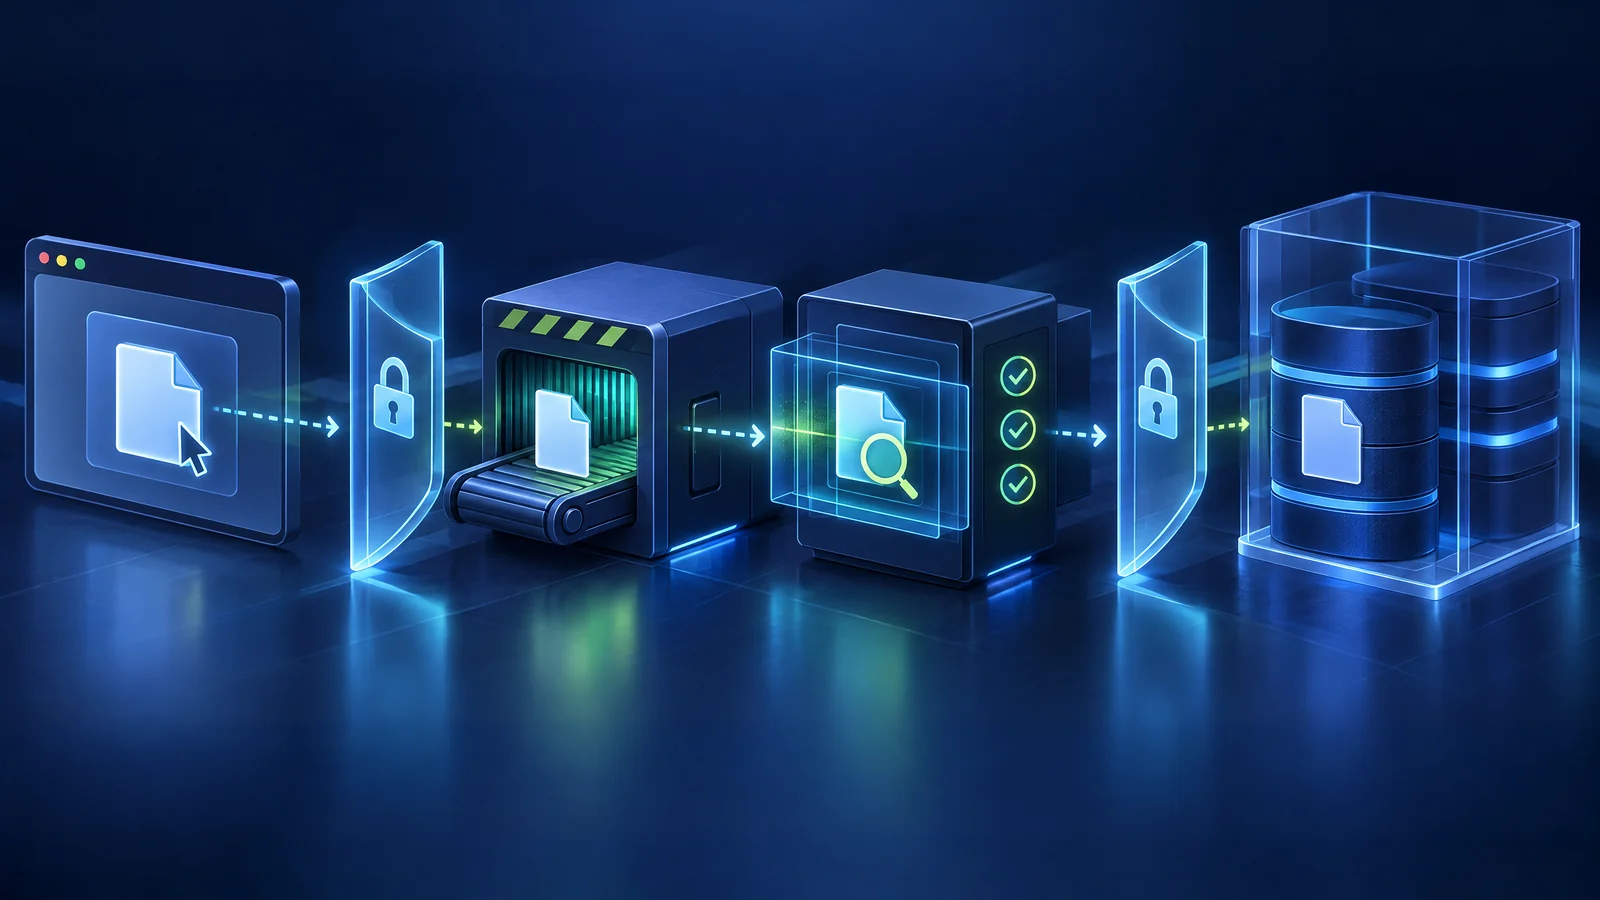
Secure file uploads are not a single validation check. Treat every upload as untrusted input and move it through an explicit state machine: authenticate the actor, enforce a narrow allowlist, inspect the bytes, quarantine the object, scan or transform it, and publish it only after a policy decision. Keep the published copy behind authorization, not a guessable URL; extensions, browser-supplied MIME types, and file signatures can each be misleading. [1]
Start with a narrow upload contract
Define what the feature actually needs before writing code. If users need profile pictures, allow a small set of image formats. If they need resumes, perhaps allow PDF and DOCX. Do not accept “any file” and hope later checks will make it safe. An allowlist reduces parser exposure and makes size, retention, and review rules testable. OWASP recommends permitting only business-critical extensions and validating input before extension checks. [1]
The browser’s accept attribute is useful guidance, not a security boundary. A client can omit it, alter the request, or send a different Content-Type. On the server, decode the submitted name, normalize it for inspection, and reject path separators, control characters, null bytes, suspicious alternate streams, and excessive length. Then generate a storage name yourself, such as a UUID. Preserve the original name only as display metadata after escaping it for the output context. This prevents user input from selecting a filesystem path or overwriting a known object. [1]
Enforce limits before expensive processing: request size, object size, number of files, and—if archives are supported—expanded size and file count. Archives are difficult to secure because extraction can amplify a small input and introduce unexpected file types. If the product does not need ZIP files, refusing them is a reasonable tradeoff.
Validate bytes, not just labels
A robust validator combines independent signals. Check the extension against the allowlist, compare the declared MIME type as a convenience check, and inspect magic bytes or parse the file with a library appropriate to the expected format. The request’s Content-Type is supplied by the client and can be spoofed; OWASP specifically warns not to trust it as the security decision. File-signature checks also should not stand alone because they can be bypassed. [1]
Parsing is an attack surface. Keep image, PDF, and office-document libraries current, restrict enabled formats, and run resource-heavy processing in a sandbox or isolated worker. For images, decoding and re-encoding can remove some unwanted content, but it is not a guarantee because the library still processes hostile bytes. Consider content disarm and reconstruction (CDR) for documents when the business can tolerate changes. [1]
A practical upload record should include an opaque ID, owner ID, display name, detected media type, byte count, checksum, storage key, scanner result, and timestamps. Keep status explicit—pending, clean, quarantined, or rejected—so an unfinished scan cannot look publishable.
Quarantine before publication
Write new objects to a private, unscanned area that application download code cannot serve. A scanner worker consumes that area and moves or copies the object to either a clean area or a quarantine area. Google Cloud’s reference deployment uses separate unscanned, clean, and quarantined buckets and triggers scanning when an object arrives. It also gives the scanner only the permissions it needs. [2]
The same separation works with other storage providers. A clean result should be an allow-to-publish decision, not a permanent claim that the file is harmless. Record the scanner and policy version, log transitions, and provide a path to re-scan clean files when definitions or rules change.
Do not email, thumbnail, index, extract, or preview a pending object unless that action is part of the isolated scanning boundary. If scanning fails or times out, keep the object unavailable and surface a retry or review state. Quarantine should be private, access-logged, and subject to retention or deletion rules so it does not become an unmanaged malware archive.
Store privately and serve deliberately
The safest default is a separate storage service or a location outside the web root. If an application must expose files, map an internal file ID to a server-generated storage key; never concatenate a user filename into a path. OWASP also recommends least-privilege filesystem permissions and warns that upload directories must not allow configuration files to change how the web server handles content. [1]
For private objects, authorize every download against the current user, tenant, role, and object state. A database row saying “owned by user 17” is not enough if the endpoint accepts an arbitrary object key. Use an application endpoint that performs the check, or issue a short-lived, object-specific download URL only after the check. AWS documents presigned URLs as time-limited bearer tokens whose capabilities are constrained by the signing principal’s permissions; anyone holding the URL can use it until it expires. [3]
When returning untrusted documents, prefer download behavior and explicit response headers. For example:
Content-Type: application/pdf
Content-Disposition: attachment; filename="resume.pdf"
X-Content-Type-Options: nosniff
Use a server-approved media type, not the client’s claim. MDN recommends X-Content-Type-Options: nosniff together with appropriate Content-Type values so browsers do not reinterpret resources as scripts or stylesheets. [4] If the product needs inline previews, put them on a separate route with a narrowly defined type policy and test the complete browser behavior.
Common mistakes and useful tradeoffs
Checking only the extension misses renamed executables and polyglot files. Checking only a magic number misses parser exploits. Scanning after publication creates a race in which another user can fetch the object first. Using the original filename as the key invites traversal and collisions. Making a bucket public turns a temporary link into a durable disclosure path. Treating a presigned URL as authorization is a mistake: it is a bearer credential, so keep its scope and lifetime narrow and never log it casually. [1] [3]
There are real tradeoffs. CDR can alter documents, image rewriting consumes CPU, and synchronous scanning increases upload latency. Asynchronous quarantine gives stronger isolation but requires a pending state and user feedback. Private storage plus mediated downloads costs application work, but it makes revocation and tenant checks possible. Choose deliberately; do not remove a control merely because the happy path is simpler without it.
FAQs
Is a client-side `accept` filter enough?
No. It improves the picker experience but does not authenticate the request or validate its bytes. Enforce the allowlist, limits, type checks, and authorization on the server. [1]
Can a malware scan make an upload safe?
No. Scanning is one layer. Keep storage private, isolate parsers, use least privilege, enforce authorization, and treat scan results as a policy decision with limits and a re-scan strategy. [1] [2]
References
[2] Automate malware scanning for documents uploaded to Cloud Storage